Remote device management (RDM) covers three operationally distinct capabilities, including policy enforcement through mobile device management (MDM), continuous monitoring and scripting through remote monitoring and management (RMM), and direct access to live or non-booting endpoints through remote and out-of-band sessions.
Most guides treat these as interchangeable, but each layer has different privilege requirements, failure boundaries, and prerequisites. By the end of this article, you’ll know what each layer does, how to route a support incident to the correct one, and which hardware and software prerequisites you need confirmed before an incident forces the decision for you.
The three-layer RDM stack
RDM operates in three tiers, each at a different depth in the endpoint and each failing independently.
MDM operates at the OS configuration and enrollment layer. It enforces policies through OS APIs, covering certificate deployment, BitLocker enforcement, application allowlisting, and conditional access. When an MDM policy fires, it calls a Windows API with no persistent third-party process running on disk. The failure boundary is the OS itself, so if Windows is enrolled and reachable, MDM works. MDM also gives a technician no live view of a user’s screen and no ability to run a diagnostic script on demand.
RMM fills that operational delta. An RMM agent is a persistent OS daemon that streams telemetry (CPU load, disk health, crash events, patch compliance) back to a cloud console and accepts inbound scripting and patching commands. It’s the layer where a sysadmin runs a PowerShell remediation across multiple endpoints at once, or gets alerted when a managed device starts logging thermal events. The failure boundary is still the OS, so if Windows won’t boot, the RMM agent can’t work.
Remote access and out-of-band recovery is the layer that survives both MDM and RMM failures. In-band remote access gives a technician a live desktop session on a running endpoint. Out-of-band (OOB) recovery goes further, operating through hardware firmware (Intel AMT on vPro platforms) and persisting even when the OS is corrupted, frozen, or absent. These two modes share the remote access category but have different prerequisites and cover different failure states.
The three tiers are complementary. MDM keeps fleet-wide policy consistent. RMM surfaces operational drift and automates remediation at scale. Remote access handles the cases automation can’t, covering live troubleshooting and hardware-level recovery when everything else has already failed.
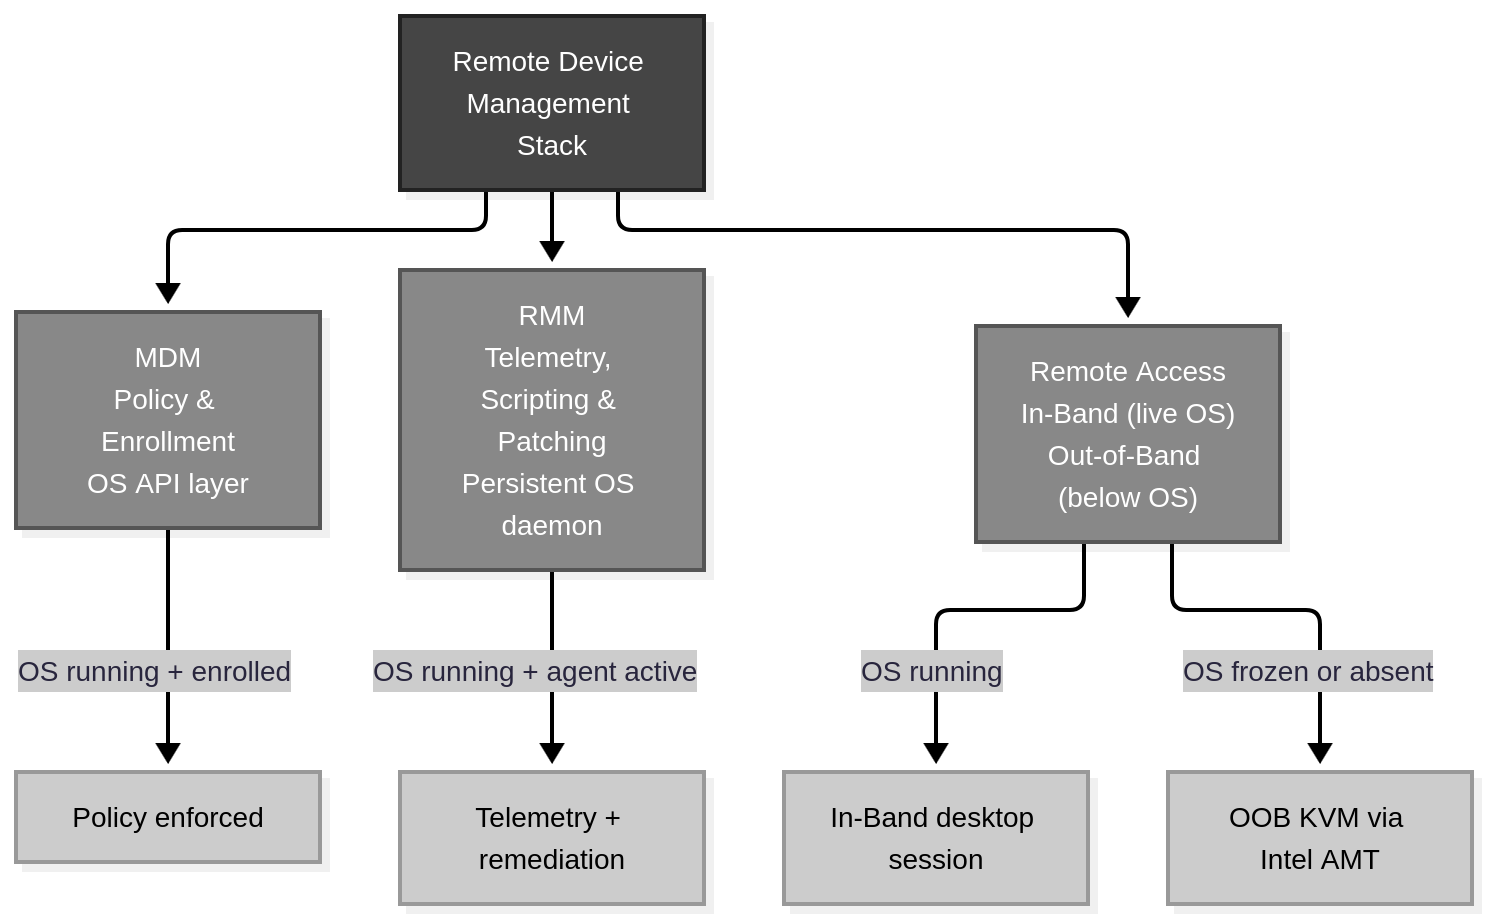
Architecture diagram showing the three-layer RDM stack. MDM and RMM both require a functioning OS. The remote access layer splits at the OS boundary, with in-band handling for live endpoints and out-of-band running through Intel AMT firmware for everything below it.
In-band support for live endpoints
The in-band path applies whenever the OS is running, and the device has network reachability. A technician initiates a live desktop session and interacts directly with the user’s environment, running diagnostics, adjusting settings, or walking through application behavior in real time. Most distributed fleet support happens day to day through this path.
The prerequisites for this path are specific: both machines need a current OS, the endpoint needs a remote-support agent with its connect plugin installed, and the technician’s machine needs a matching viewer client.
- Both the technician’s machine and the recipient’s endpoint must run Windows 11
- The endpoint needs a current remote-support agent with its connect plugin deployed (in HP Workforce Experience™ Platform (WXP), for example, the Insights Agent, with Remote Connect Plugin Package)
- The technician’s machine needs a matching viewer client
Network requirements are outbound-only, so home office deployments behind consumer-grade routers don’t require inbound port exceptions or VPN tunnels:
- Technician’s machine: outbound TCP 443 and TCP/UDP 4172
- Recipient endpoint: outbound TCP 443 and UDP 55000, with the local endpoint binding UDP 4172 as the outbound source port (confirm your local firewall policy allows that binding)
- No inbound ports, no VPN requirement
For the full FQDN allowlist, check your platform’s network-requirements documentation.
A pixel-streaming connection keeps the session itself out of the data path. Only encrypted display pixels cross the wire, so no files, clipboard data, or credentials leave the recipient’s machine. A technician sees exactly what the user sees and can share keyboard and mouse control, with multi-monitor support through a dropdown toolbar.
Out-of-band recovery for non-booting endpoints
The OOB path handles endpoints where the OS is frozen mid-boot, corrupted by a bad patch, missing after a failed reimaging attempt, or stuck on a blue screen with no visible recovery option. When the OS can’t load, software-based agents, including RMM daemons and in-band remote access clients, can’t fire. The OOB KVM channel persists because it runs in Intel AMT firmware on the Intel CSME subsystem, independent of the host OS and processor state.
Two hardware prerequisites apply:
- Intel vPro Enterprise processor (8th generation or later) with Intel AMT enabled in BIOS and current Intel CSME firmware applied
- Network connection through a native Intel wired or Intel wireless vPro NIC
That second point catches teams off guard because USB-to-Ethernet adapters and most docking-station Ethernet ports aren’t supported for OOB connections (some Thunderbolt 4 docks are an exception, so verify the specific model before ruling a device out).
A device plugged into an unsupported USB hub or dock loses OOB network access, so you can’t initiate an AMT session even if the hardware otherwise qualifies. Check NIC support before provisioning OOB capability across your fleet. Windows 10 or later is required for the initial agent enrollment that binds the endpoint to the cloud management instance.
On the software side, the endpoint needs a current remote-support agent with its out-of-band connect plugin installed. These deploy automatically when tenant updates are set to Automatic.
Once an OOB session is established, the technician has full BIOS-level KVM control, meaning keyboard, video, and mouse redirection at the firmware layer. They can power-cycle the device, enter BIOS/UEFI to adjust settings, invoke the boot menu, and view the display regardless of OS state. Because the AMT processor shares a direct hardware bus with the GPU pipeline, it captures and streams display output even during reboot sequences and BIOS screens.
Choosing the right recovery path
Two questions determine which path applies. Is the OS booting? Is the network reachable? Both must be yes for an in-band session to work. If either answer is no, OOB is the only path that reaches the device.
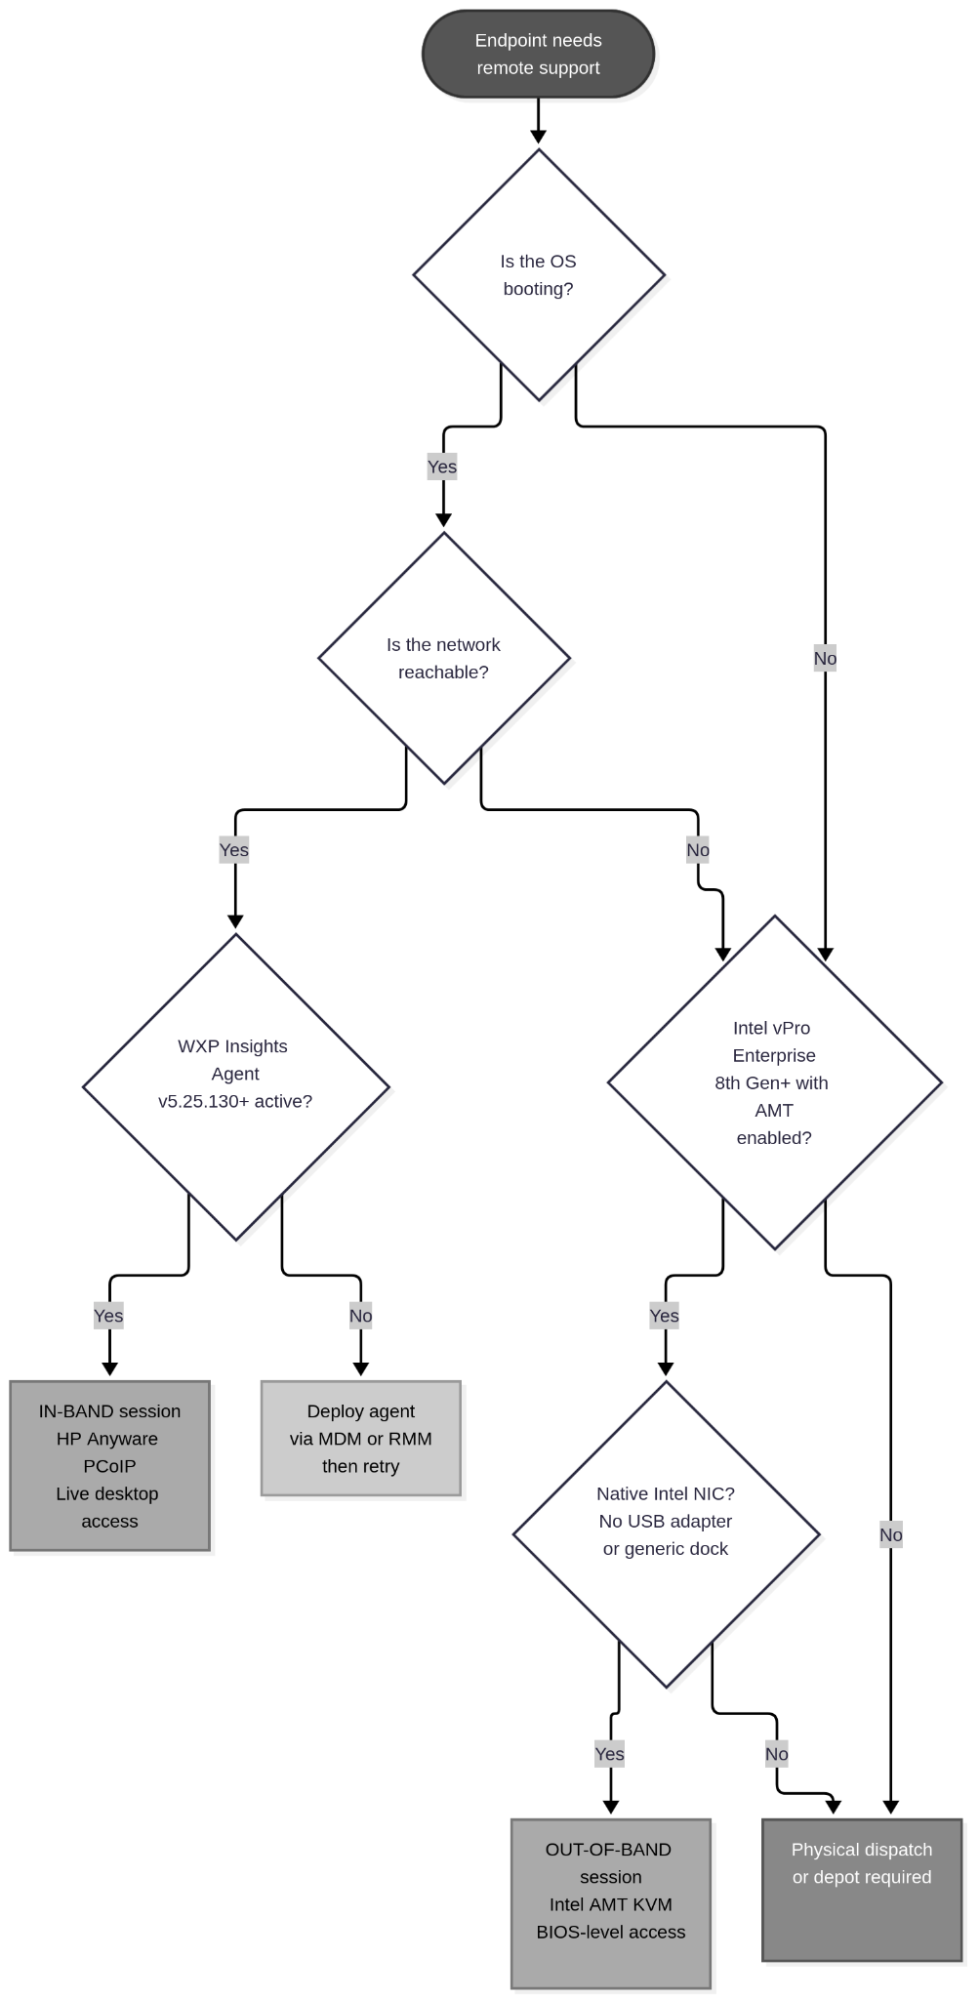
Decision tree for routing any support incident through these two questions. Both branches can be initiated from the same console, and the platform routes to the correct channel based on device state.
Verification, RBAC, and user consent
Remote access of either kind should be gated to a small set of support-tier roles rather than opened up to every console user. In WXP, for example, that gate covers five roles: IT Admin, Helpdesk, Helpdesk Lite, Partner Administrator, and Service Specialist. An account outside that list can’t start a session no matter what other permissions it holds elsewhere in the console.
The consent model differs between session types, and both are designed to prevent covert access.
For in-band sessions, the recipient usually gets a consent pop-up when the technician requests a connection. Only after the recipient accepts does a one-time session code appear on their screen. The recipient then shares the code with the technician, by phone or chat, before the session opens.
For OOB sessions, the hardware itself enforces consent instead of the OS. A firmware-generated code typically renders directly on the client monitor, visible even at a BIOS screen, mid-boot, or on a frozen blue screen, and the recipient reads it to the technician before any KVM control is granted.
Frequently asked questions
What is remote device management?
Remote device management is a set of capabilities that lets IT teams configure, monitor, and access endpoints without being physically present. It covers three functional layers, including policy enforcement through MDM (which applies OS-level configuration via platform APIs), operational monitoring and scripting through RMM (which runs a persistent agent daemon to stream telemetry and execute remediation scripts), and remote access and recovery (which gives technicians live desktop sessions for running endpoints and hardware-level KVM access through Intel AMT firmware for endpoints that won’t boot).
What is the difference between MDM and RMM?
MDM uses OS enrollment APIs to push configuration policies, including certificate deployment, security baselines, and application control. It requires no persistent third-party process and operates at the OS configuration layer. RMM runs a persistent daemon on the endpoint that continuously streams telemetry (device health, patch state, crash logs) to a cloud console and accepts on-demand scripting and patching commands from the administrator. MDM enforces the desired state while RMM surfaces drift from that state and provides the operational tooling to correct it. Both belong in a complete remote management architecture.
What is out-of-band device management?
Out-of-band device management is hardware-level remote access that runs through Intel AMT firmware on Intel vPro Enterprise platforms, independent of the host OS. Because Intel AMT operates on the Intel CSME subsystem and shares a direct hardware path to the GPU, it can capture display output, accept keyboard and mouse input, and execute power commands even when the host OS is corrupted, absent, or frozen. Administrators can access BIOS/UEFI settings, power-cycle the device, and observe boot sequences, giving them capabilities software-based agents can’t provide once the OS layer fails.
Next steps for remote device management
Remote device management across a distributed Windows fleet requires three layers working in concert: MDM for consistent policy enforcement, RMM for continuous operational visibility and scripted remediation, and remote access for cases where automation has reached its limit. Routing an incident to the wrong layer wastes time, whether that means running an RMM script against an endpoint that won’t boot or dispatching a technician to a site recoverable via OOB KVM.
To see how WXP unifies remote management across your fleet, visit workforceexperience.hp.com. Developers can explore API and integration documentation at developers.workforceexperience.hp.com.